NodeOps Security Infrastructure · Assurance
Accepting new engagements

Security and infrastructure engineering for teams that can’t afford downtime.

NodeOps Security OÜ is a remote-first B2B consultancy. We audit, harden and operate the Linux and Windows systems your business runs on - then help you put the policies in place that keep them that way.

Registered
Estonia, EU
Delivery
100 % remote
Coverage
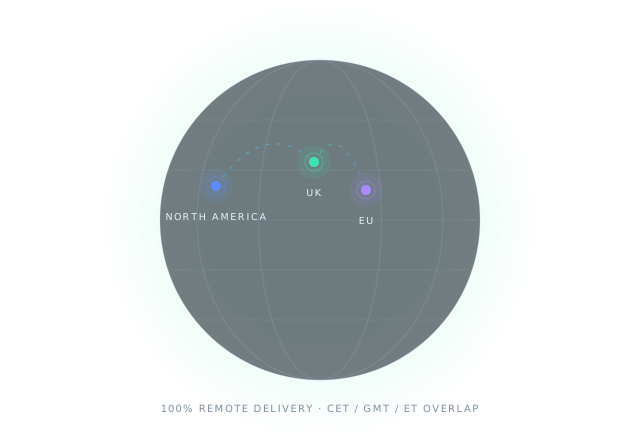
EU · UK · North America
Activity
EMTAK 62201
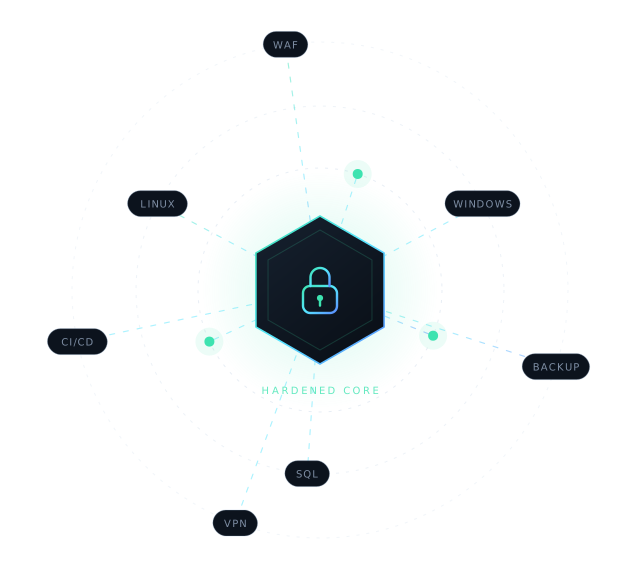
A hardened core surrounded by the services we monitor and maintain: Linux and Windows hosts, databases, CI/CD, VPN, WAF and backups.
Estonian private limited company (OÜ) 100 % remote delivery EU · UK · North America Least-privilege, time-boxed access First reply within one business day
What we do

One team from the risk register down to the shell prompt.

Most providers stop at either strategy or implementation. We do both, which means the controls we recommend are ones we know how to run - and the systems we run are built to satisfy the controls.

Technical security audits

A hands-on review of what an attacker would actually reach, ranked by the damage it would do.

  • External and internal attack surface
  • Server and OS hardening review
  • Identity, access and privilege paths
  • Written findings with a fix for each one
Details about Technical security audits

Linux infrastructure

Debian, Ubuntu, RHEL, Rocky and Alma estates built to be boring, repeatable and patched.

  • Provisioning and configuration management
  • Nginx, Apache, PHP-FPM and Node stacks
  • DNS, mail, TLS and certificate lifecycle
  • Monitoring, logging and alert tuning

Details about Linux infrastructure

Windows infrastructure

Active Directory and Windows Server estates cleaned up, baselined and kept current.

  • Active Directory review and hardening
  • Group Policy baselines
  • Patching, Defender and endpoint policy
  • Backup and restore validation

Details about Windows infrastructure

Database optimisation

Finding the queries, indexes and settings that are quietly costing you money and uptime.

  • PostgreSQL, MySQL and MariaDB
  • Slow query and index analysis
  • Replication, failover and PITR backups
  • Capacity and growth planning

Details about Database optimisation

DevOps support

Pipelines, infrastructure as code and release process that your team can run without us.

  • CI/CD pipelines and build hygiene
  • Terraform and Ansible automation
  • Containers and environment parity
  • Secrets handling and rotation

Details about DevOps support

Managed operations

An ongoing retainer for the infrastructure work nobody on your team has time to own.

  • Proactive patching and monitoring
  • Incident response and escalation
  • Documented runbooks you keep
  • Monthly reporting in plain language

Details about Managed operations

Also part of the job

Security decisions that survive contact with the business.

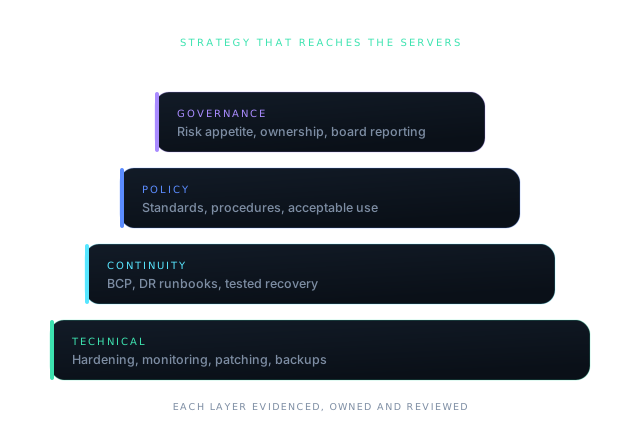
A hardened server does not help much if nobody knows who owns it, what it holds, or what happens when it is gone for a day. Alongside the technical work we advise on risk management, corporate security policy and business continuity - the layer above the implementation.

  • Risk registers with named owners and real treatment plans
  • Policy sets written to be followed, not filed
  • Continuity and recovery plans that get tested
  • Control mapping for ISO/IEC 27001, NIS2 and the CIS Controls

Explore our consulting practice

Four connected layers: governance, policy, continuity and technical controls.
How we work

Predictable engagements, in four steps.

No open-ended discovery, no surprise invoices, no access we cannot justify.

  1. Scope

    A short call, then a written scope: what we will look at, what we need access to, what you receive, and what it costs. Fixed fee wherever the work allows it.

  2. Assess

    Hands-on review with read-only access first. We verify findings before reporting them, so you are not chasing false positives from a scanner.

  3. Remediate

    Findings ranked by real-world impact, each with a concrete fix. We implement them, or hand your team runbooks precise enough to follow.

  4. Operate

    Optional retainer: patching, monitoring, incident response and a monthly report that a non-technical director can read.

Where we work

Remote by design, not by circumstance.

We were built as a distributed company from day one. There is no office overhead priced into our rates, no travel days on your invoice, and no waiting for someone to be in the building before a production issue gets looked at.

EUROPEAN UNIONUNITED KINGDOMNORTH AMERICAENGLISH · PORTUGUESE · FRENCH
A stylised globe marking our delivery coverage across North America, the United Kingdom and the European Union.
How to engage us

Three ways to work together.

01 - PROJECT

Audit or project

A defined piece of work with a fixed scope and a fixed fee: a security audit, a migration, a database rescue, a continuity plan.

  • Written scope before work starts
  • Fixed price, no hourly drift
  • Report and remediation plan included

02 - RETAINER

Ongoing management

A monthly block of hours for the infrastructure nobody internally has time to own, with agreed response times.

  • Proactive patching and monitoring
  • Named escalation path
  • Monthly reporting

03 - ADVISORY

Strategic advisory

Scheduled sessions for leadership who need a technical second opinion before committing budget or signing a contract.

  • Risk and architecture review
  • Supplier and tooling due diligence
  • Board-ready summaries
Questions

The things clients ask first.

How does an engagement usually start?

With a short call and a written scope. We agree what is in and out, what access we need and what you get at the end, before any work begins. Audits and projects are quoted as a fixed fee; ongoing work runs as a monthly retainer.

What access do you need to our systems?

The least we can do the job with. Reviews start read-only. Anything that changes state is agreed in writing first. Access is tied to named accounts, time-boxed to the engagement and revoked when it ends - and we are happy to work inside your own jump host, VPN or PAM tooling rather than ours.

Do you certify us against ISO 27001 or NIS2?

No - certification is issued by an accredited body, and it would be a conflict of interest for the people who built your controls to audit them for certification. What we do is get you ready: gap analysis, the control and policy work, and the evidence structure an auditor will ask for.

We already have an IT provider. Does that make this awkward?

Not usually. A lot of our work sits alongside an existing provider or in-house team - an independent audit, a database that nobody has had time to tune, or continuity planning that keeps getting pushed back. We write findings to be actionable by whoever owns the system, and we are happy for that to be someone else.

Which time zones do you work in?

We operate on Central European Time, which gives a full working-day overlap with the UK and the rest of the EU, and a solid afternoon overlap with the Eastern and Central United States and Canada. Maintenance windows are scheduled around your business hours, not ours.

Will you sign an NDA and a data processing agreement?

Yes to both, and we would rather you asked. We can work from your paper or provide ours. As an EU-registered company we are used to GDPR obligations and can document the technical and organisational measures that go with them.

Let’s find out what is actually exposed.

Tell us what you run and what keeps you up at night. You will get a written scope and a fixed price - and a reply within one business day.